Your partner on the path to NIS2 compliance
Bringing TailoredGuard to Poland & CEE
P-REC is the lead partner of TailoredByte in Poland and Central & Eastern Europe. We help organizations in regulated sectors achieve full NIS2 compliance through an AI-powered platform.
P-REC: Your partner
in the era of AI & NIS2
P-REC is a Polish technology company specializing in deploying security solution standards for organizations operating in regulated sectors. As the lead partner of TailoredByte in Poland and Central & Eastern Europe, we offer comprehensive support in achieving full NIS2 compliance.
TailoredGuard Technology & Expertise
As the lead partner of TailoredByte in Poland, P-REC offers the TailoredGuard platform, combining AI-powered automation with hands-on expert support, giving organizations real tools to achieve and maintain NIS2 compliance.
AI Engine
The platform is built on an advanced AI module that continuously analyzes your organization's security posture against NIS2 requirements, flagging areas that need attention.
Proactive Management
Instead of reacting to incidents after the fact, the platform actively plans schedules, assigns tasks, and tracks progress, eliminating chaos and ensuring full transparency.
Experts by Your Side
Our team of cybersecurity and NIS2 implementation specialists is available at every stage, from the first audit to ongoing consultations and compliance process optimization.
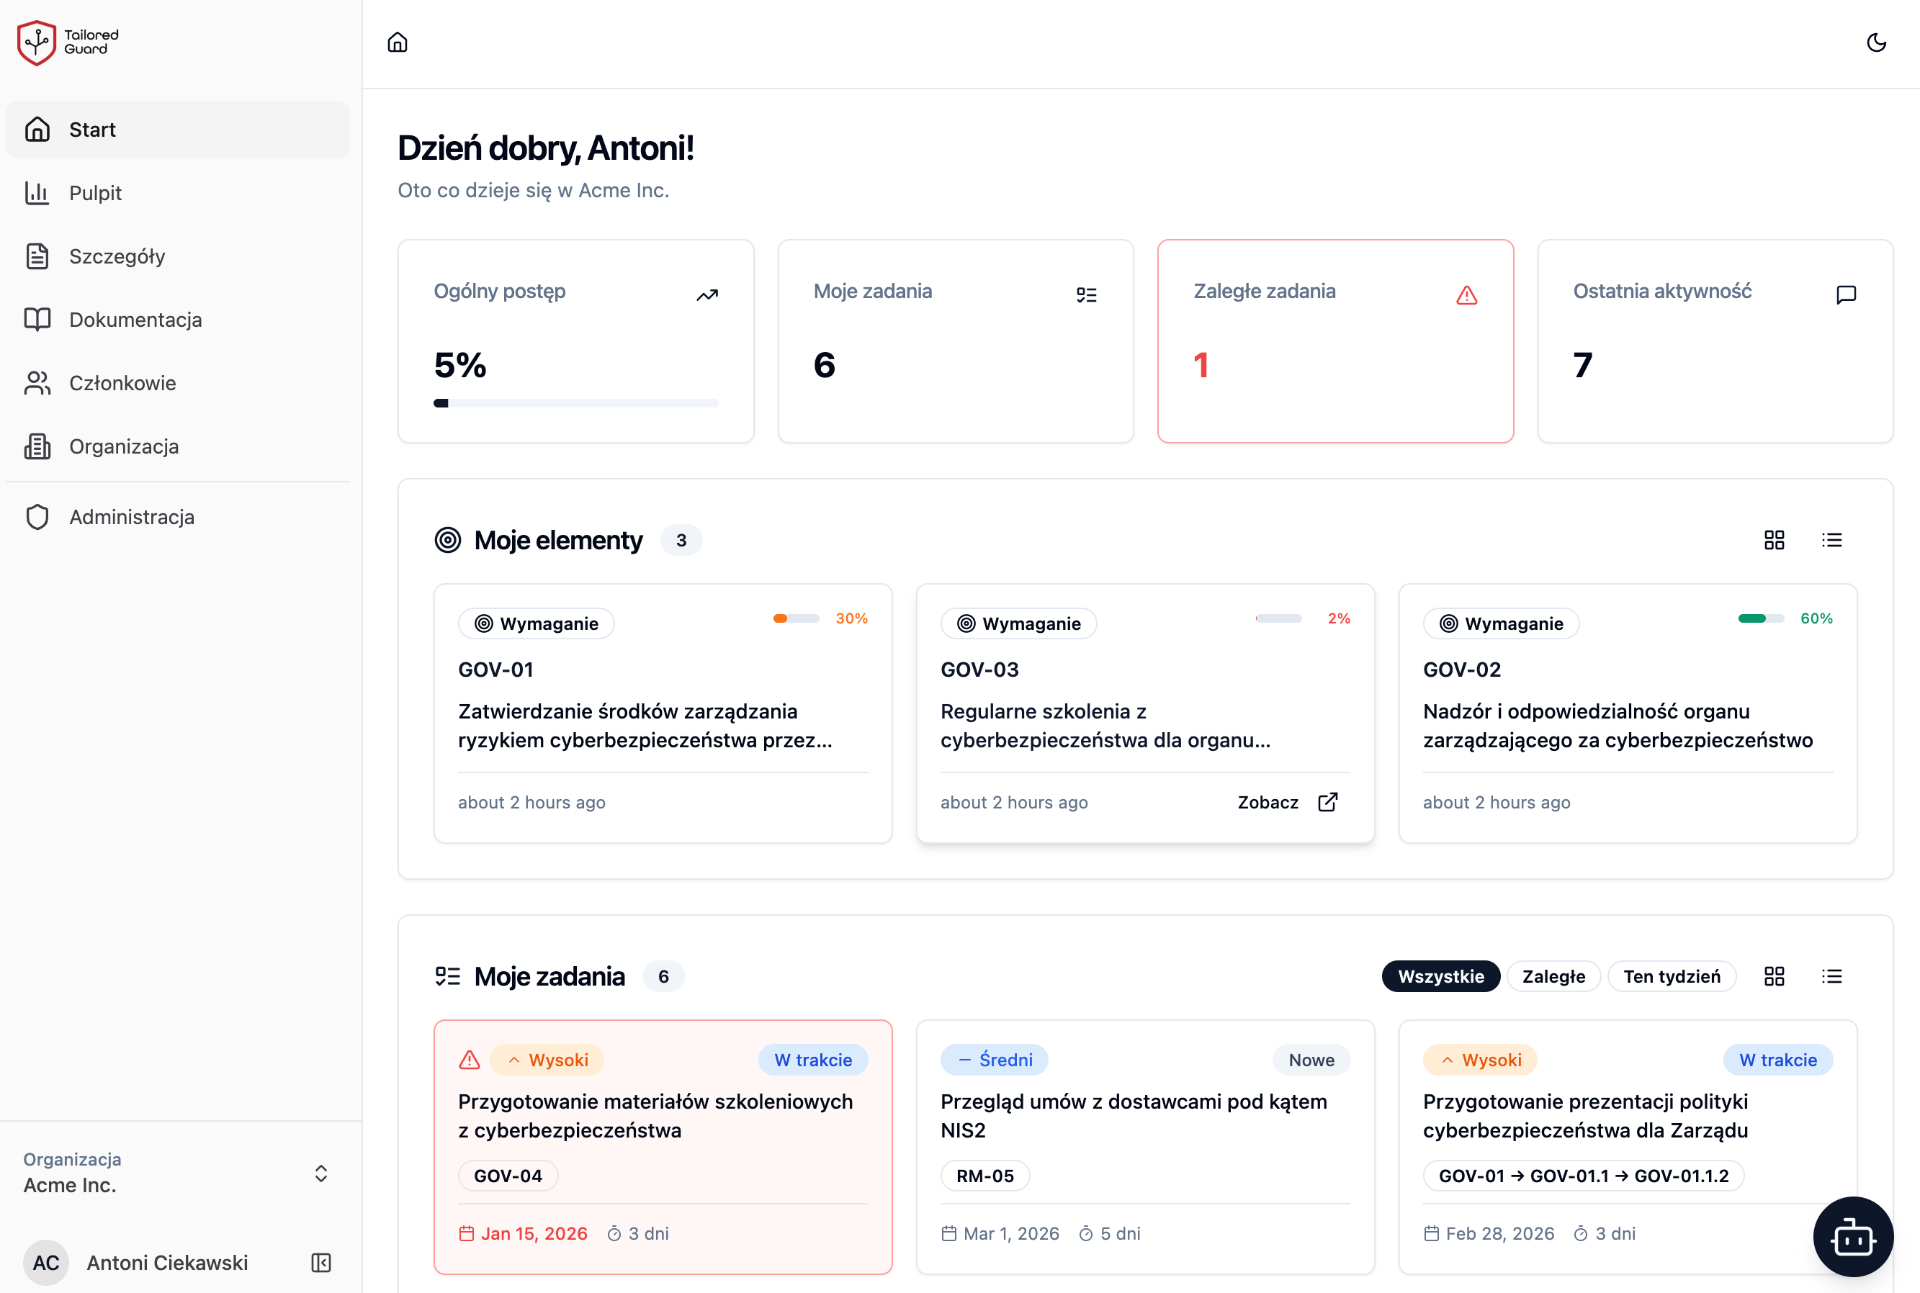
Platform in action
Your organization must
meet NIS2 requirements
Poland's implementation of the NIS2 directive requires organizations in critical sectors to implement comprehensive cybersecurity measures. Company boards bear direct legal responsibility for the state of security. Unprepared organizations risk severe sanctions.
From the enforcement date (03.04.2026) national supervisory authorities may impose the first financial penalties
TailoredGuard mapping to NIS2 requirements
Act now
We'll conduct a free NIS2 compliance consultation for your organization.
Book a consultation →Deploy the platform
Deploy TailoredGuard and achieve full NIS2 compliance through automation and expert support.
See the process →Be audit-ready
Automated documentation and NIS2 reports ready for any supervisory authority request.
Learn more →Is your organization
covered by the NIS2 directive?
The NIS2 directive covers essential and important entities across 18 sectors. If your organization uses AI systems, you have an obligation to implement appropriate security measures.
Critical sectors
Other important sectors
Real-world examples
Examples of entities from NIS2-covered industries
Banking & financial institutions
Banks, credit unions, investment firms, and payment operators are Essential Entities in the financial sector. Protection of transaction systems, online banking, and 24-hour incident reporting under NIS2 and DORA is required.
Energy & power distribution
Operators of electricity, gas, and heating networks, as well as energy producers (including renewables and PV farms above thresholds) are Essential Entities. Full protection of SCADA, OT systems, and critical infrastructure is required.
Hospitals & healthcare
Healthcare facilities (hospitals, clinics, medical centers, laboratories) are Essential Entities in the health sector, regardless of size. Full NIS2 compliance, 24-hour incident reporting, GDPR-protected medical data, and HIS/EHR security are required.
Transport & logistics
Freight forwarders, road, rail, and air carriers, port operators, and logistics terminals are Essential or Important Entities. Protection of fleet management, EDI terminals, and traffic control systems is required.
Public administration
Central authorities, local governments, and public sector institutions providing e-government services are Essential Entities. Protection of state registries, e-government platforms, and citizen data is required.
Digital infrastructure & telecoms
Telecom operators, ISPs, data centers, DNS providers, IXPs, and CDNs are Essential Entities. Full protection of backbone networks, business continuity, and incident reporting to CSIRT are required.
Industrial manufacturing & sawmills
Manufacturing plants, sawmills, wood processing, furniture makers, metal and plastics producers with 50+ employees or €10M+ turnover are Important Entities. Protection of IT/OT, SCADA, and supply chain is required.
Chemicals & pharmaceuticals
Manufacturers of chemicals, drugs, supplements, and distributors of pharmaceuticals are Important Entities. Securing production systems, laboratory systems (LIMS), and active substance supply chains is required.
Waste management & recycling
Companies collecting, processing, and disposing of municipal, industrial, and hazardous waste are Important Entities. Protection of waste-tracking systems, weighing systems, and installation monitoring is required.
Space sector
Satellite operators, navigation providers, Earth observation, and satellite communication services are Essential Entities. Protection of ground stations, the space segment, and telemetry data transmission is required.
Digital technologies & SaaS
Providers of cloud services, e-commerce platforms, search engines, social media, and B2B SaaS are Important Entities. NIS2 compliance for service continuity, customer data protection, and incident management is required.
Postal & courier services
Postal operators, courier companies, and e-commerce fulfillment providers are Important Entities. Protection of track&trace, fleet management, dispatch terminals, and recipient data is required.
Three steps to full compliance
and cyber resilience
Our proven implementation process ensures rapid NIS2 compliance without disrupting your organization's daily operations.
Audit & Deployment
Our experts deploy the TailoredGuard platform in your organization and conduct an initial audit. The AI module maps your current security posture to NIS2 requirements, identifying specific gaps and action priorities.
Planning & Automation
Based on audit results, the platform configures automated schedules, assigns responsibilities, and launches cyclical compliance processes. Your team focuses on action, not administration.
Continuous Monitoring & Reporting
After deployment, the platform continuously tracks compliance status, generating deviation alerts and automatically compiling documentation required by supervisory authorities.
Start acting
today
Book a free consultation and TailoredGuard platform demo.
What do you get for free?
- NIS2 compliance consultation
- TailoredGuard platform demo
- AI security gap report
- NIS2 implementation roadmap
- Cybersecurity expert consultation
